
Clarity beats complexity
If nobody understands a management system, it does not work. We explain terms, requirements and decisions in plain language.
About
FeldmannCyber GmbH is a consulting and software company for information security, management systems and compliance, based in Griesheim near Darmstadt, Germany. We work with organizations across Germany and Europe.
Our focus is information security management systems based on ISO/IEC 27001 — from building them to operating and improving them. On top of that we work on quality management (ISO 9001), integrated management systems, cybersecurity compliance and AI governance.
We have seen management systems end up as piles of documents nobody understands. That is why we work differently: alongside internal teams, with the tools that already exist, and with the goal that the organization can carry its ISMS itself.
We also develop the FeldmannCyber App — software that supports the work around the ISMS, including curated databases of cybersecurity vendors and funding programs.
If nobody understands a management system, it does not work. We explain terms, requirements and decisions in plain language.
We work with you instead of inspecting from outside. Our customers should say “they work with us” — not “they audit us”.
Your ISMS should belong to your organization — not your consultant. We build internal capability instead of dependency.
We use what works and improve what doesn’t — without unnecessary new platforms.
European where possible. Open where practical. Integrated with what already works.
We are not a law firm, a SOC or a forensics provider. Where specialists are needed, we say so and help you find the right ones.
FeldmannCyber was founded by Alexander Feldmann and Beste Meltem Feldmann, who lead the company together.
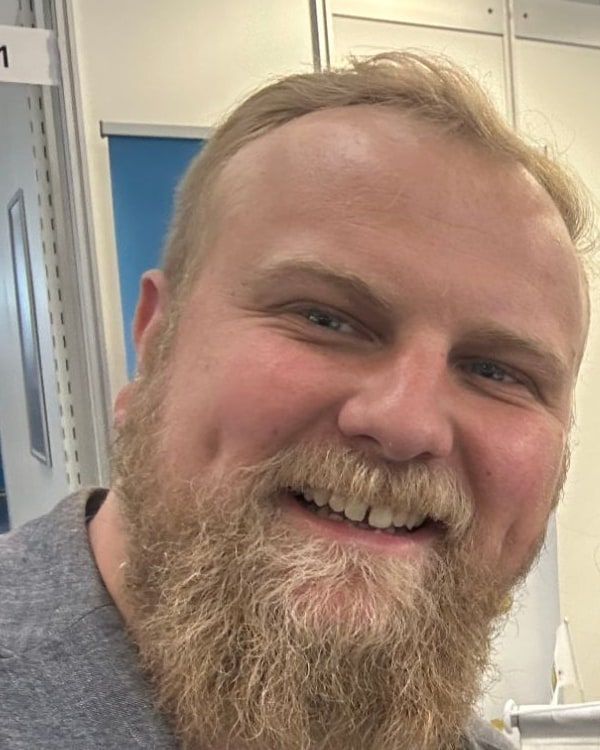
Co-founder & Managing Director
As an ISO 27001 Lead Implementer, cybersecurity consultant, and software developer, I combine technical depth with the practical mindset of a founder. I help businesses turn complex security requirements into workable processes and approach AI adoption with security, risk, and business value in focus. My strength is connecting technology, compliance, and execution—making ISO 27001 implementation and AI consulting practical, actionable, and aligned with your business goals.
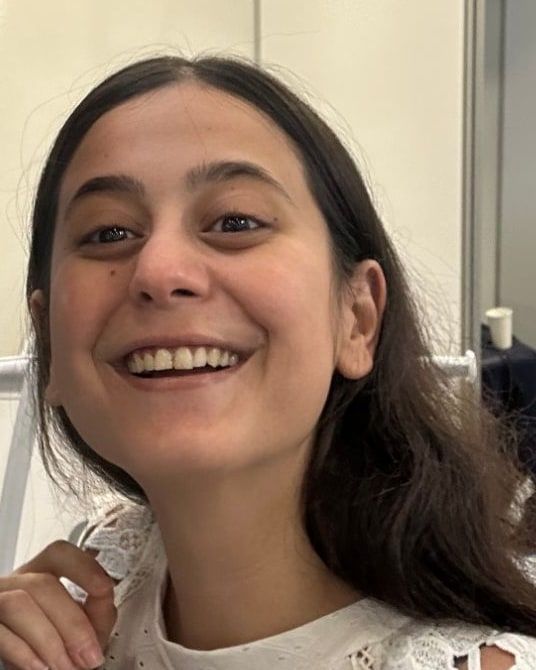
Co-founder & Managing Director
As a seasoned project manager, I bring structure, clarity, and momentum to complex projects. I complement my husband’s technical and cybersecurity expertise by coordinating stakeholders, managing timelines, and keeping delivery on track. Together, we help businesses translate ISO 27001 requirements and AI ambitions into clear plans, coordinated action, and practical results.
Cybersecurity, standards and regulation produce a lot of noise: jargon, requirements, alarming headlines and vendors who all promise everything. Our job is to turn that noise into clear choices — what matters for your organization, what to do first and which option fits. In German we say it as “Klarheit im Cyberdschungel”: clarity in the cyber jungle.
We help build and maintain practical management systems such as ISO/IEC 27001 and ISO 9001 — designed around how your organization already works.
When the ISMS identifies a risk, gap, control or improvement, we help determine the right next step and implement it — process, people or technology.
We take part in the work instead of handing over a task list: workshops, working sessions, coordination and follow-up alongside your people.
We explain, train and transfer knowledge while doing the work — so your team can increasingly run and improve the ISMS itself.
A first conversation is non-binding. Tell us what you’re working on.